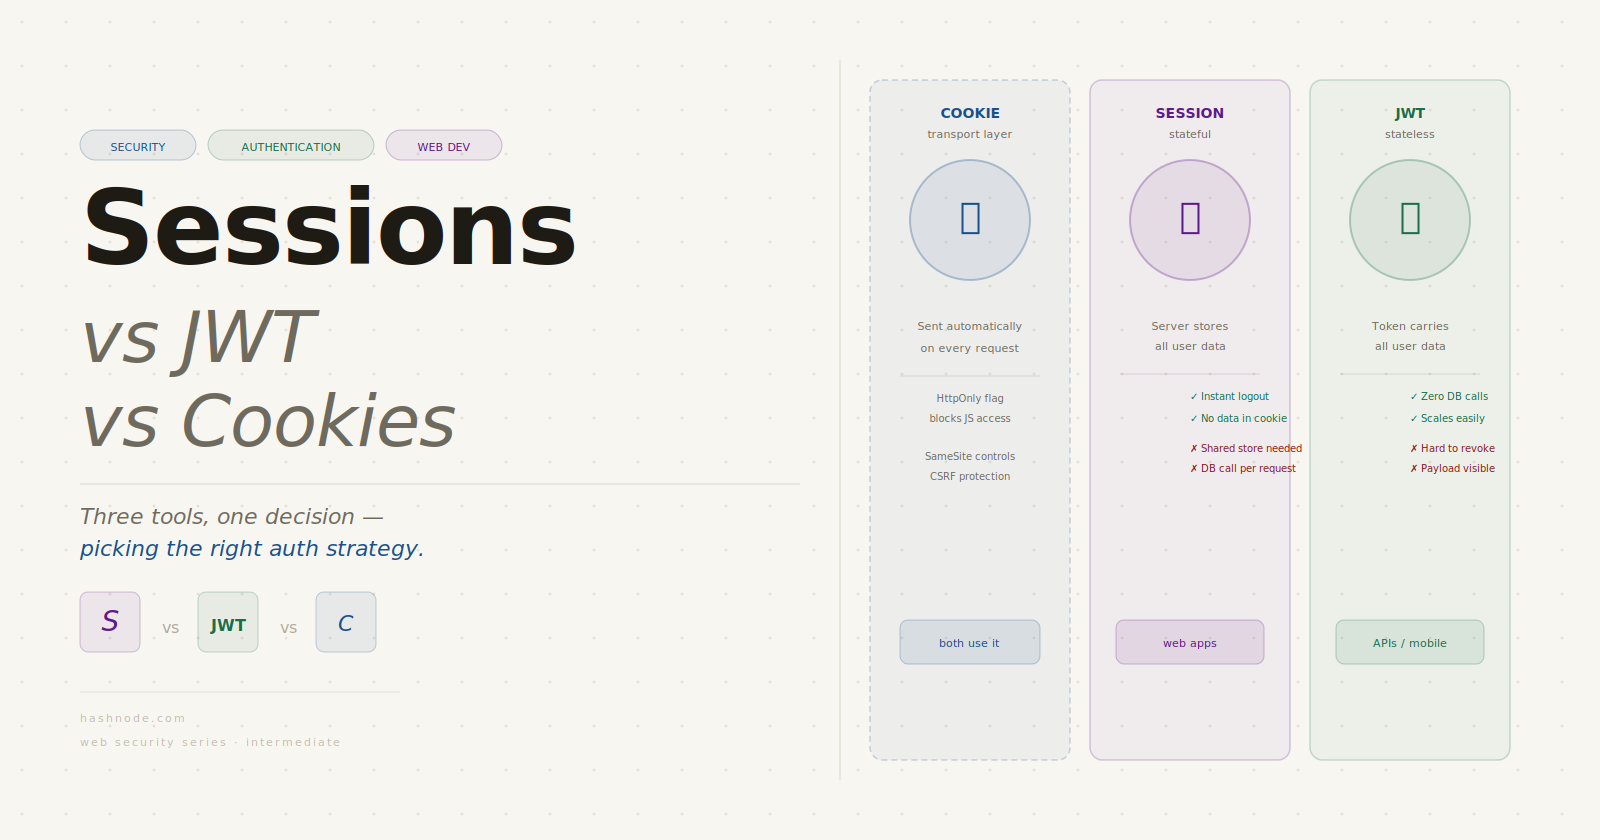
Every web app needs authentication — but choosing between sessions, JWTs, and cookies trips up even experienced developers. This guide cuts through the confusion: what cookies actually are (hint: just transport), how session-based auth stores state on the server, how JWTs pack everything into a self-contained token, and the real-world tradeoffs that determine which one belongs in your architecture. One comparison table, two flow diagrams, and one clear mental model.